Ledger Security Breach: The Impact on B2B Event Trust
Ledger Security Breach: The Impact on B2B Event Trust
When hardware security fails, trust becomes the most valuable asset at any high-stakes B2B event. The discovery of unauthorized hardware implants in Ledger devices sold via third-party channels has sent ripples through the tech and fintech sectors. For event organizers, this isn't just a technical glitch; it is a fundamental threat to the integrity of the attendee experience. In an era where physical swag often includes sophisticated technology, the supply chain is now a critical security perimeter that requires rigorous oversight and expert management.
How does the Ledger hardware breach impact trust at major crypto events?
The confirmation by Ledger that an unauthorized hardware implant was discovered in a device sold by CryptoBilis—a breach resulting in losses estimated between $86 million and $93 million—has fundamentally altered the risk assessment for international B2B summits. In the high-stakes world of blockchain and decentralized finance, events like Consensus or EthCC serve as more than just networking hubs; they are distribution points for the very tools meant to secure the industry's assets. When a trusted name like Ledger faces a supply chain compromise, it forces a radical re-evaluation of every physical touchpoint at a conference. Security is no longer confined to the digital realm of Wi-Fi encryption or badge scanning; it now encompasses the physical integrity of every piece of hardware handed out in a VIP lounge or a sponsor hall.
This incident highlights a critical vulnerability: the 'halo effect' of premium events. Attendees often lower their guard within the confines of a high-tier conference, assuming that the organizers have vetted every sponsor and every gift. If a device received at a premier event is compromised, the reputational damage is not limited to the hardware manufacturer; it extends to the event brand itself. We are entering an era where 'security theater' is no longer sufficient. Organizers must now implement rigorous supply chain audits that track technology from the factory floor to the attendee's hand. The financial and legal fallout of a breach originating at a summit can be catastrophic, potentially leading to class-action litigation and a permanent loss of institutional trust. For the C-suite executives and high-net-worth individuals who frequent these gatherings, physical security is now a non-negotiable technical requirement.
Furthermore, the Ledger breach demonstrates that the threat landscape is evolving toward physical intervention. While software exploits can often be patched remotely, a hardware implant is a permanent, physical backdoor that bypasses traditional digital defenses. This requires a shift in event planning logic. Organizers must move away from the convenience of local resellers and toward direct-from-manufacturer relationships. The cost of a compromised device is not measured in the price of the hardware, but in the total value of the assets it is meant to protect. In the context of a B2B event, where billions of dollars in AUM (Assets Under Management) may be represented in a single room, the stakes could not be higher. Trust must be defended at every stage of the event lifecycle, from procurement to the final keynote.
What are the security risks of distributing hardware swag at B2B conferences?
Distributing hardware swag—ranging from encrypted USB drives to hardware wallets and specialized tablets—has long been a staple of tech conferences in global hubs like Singapore, Dubai, and London. However, the Ledger incident has exposed the 'man-in-the-middle' (MITM) vulnerability inherent in large-scale event logistics. When an agency or organizer sources thousands of items, the temptation to use third-party resellers to meet budget constraints or delivery timelines is high. This is precisely where the risk resides. An unauthorized implant is not a coding error; it is a deliberate physical modification designed to intercept private keys or sensitive data before it ever reaches the end-user. For a marketing director, the nightmare scenario is providing the very conduit for a multi-million dollar theft.
As highlighted in recent BizBash trends: Security and technology in event planning, the integration of high-tech gifts now requires a level of technical due diligence that many event agencies are currently unequipped to provide. The risk profile has shifted from logistical delays to existential threats. If an event is identified as the point of origin for a security breach, the legal implications regarding 'duty of care' become central. Organizers must now demand comprehensive chain-of-custody documentation. This includes tamper-evident packaging, serial number verification against manufacturer databases, and secure transit protocols. The 'cheapest bidder' model is officially obsolete in the context of tech-heavy giveaways.
Moreover, the complexity of modern hardware means that visual inspection is often useless. A modified Ledger device looks identical to a genuine one to the naked eye. This necessitates a 'Zero Trust' approach to event swag. Organizers should consider whether the distribution of high-risk hardware is even necessary, or if it can be replaced by digital vouchers that allow attendees to order directly from the manufacturer's secure portal. If physical distribution is required, it must be accompanied by a transparent security protocol that attendees can verify. Every item in an attendee's gift bag is a direct reflection of the host's brand integrity. In 2026, a single compromised device can negate years of brand building and community trust.
How can event organizers ensure attendee safety following high-profile security incidents?
Safety in the post-Ledger landscape is defined by radical transparency and proactive communication. To rebuild trust, organizers must adopt a 'verify, then trust' stance. This involves making the event's security protocol a headline feature rather than a background process. For instance, discussions on LinkedIn regarding Ledger security and event industry impact suggest that on-site verification stations—where experts can help attendees verify the firmware and physical integrity of their devices—may soon become a standard requirement at major tech summits.
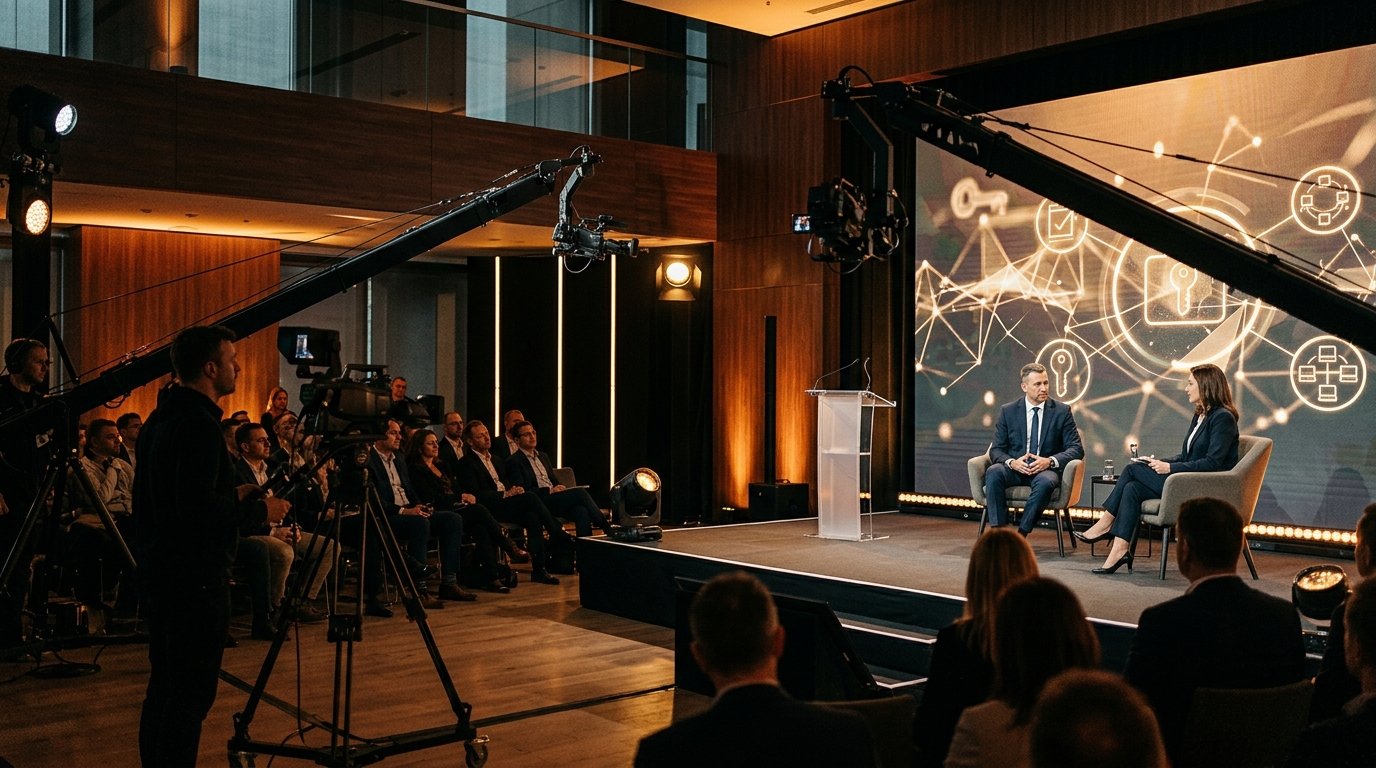
As the premier visual storytellers for major crypto summits like EthCC and Consensus, Alesia RSVP operates at the intersection of physical security and digital trust. We understand that in a high-stakes environment, how a brand handles security is as important as the security itself. We document the rigorous standards and technical measures taken by organizers, providing the visual evidence needed to reassure a skeptical audience. Whether it is capturing the unboxing of certified hardware or streaming a security keynote that addresses these risks head-on, our high-quality production serves as a testament to an organizer's commitment to attendee safety. Professional documentation is not just about marketing; it is about creating a transparent record of due diligence.
To effectively mitigate the fear caused by industry-wide breaches, organizers should also implement 'Security Briefings' for attendees, similar to safety demonstrations on an aircraft. These briefings should cover how to identify genuine hardware, how to report suspicious activity, and the specific steps the event has taken to secure the supply chain. By documenting these efforts through professional video and editorial content, brands can control the narrative and demonstrate leadership. In an era of heightened skepticism, the most effective way to protect a brand's future is to prove, through clear and professional evidence, that attendee safety is the top priority. Trust is no longer a given; it is a technical and editorial achievement that must be earned through every interaction.
FAQ
Is it safe to accept hardware wallets as event swag after the Ledger incident?
It is only safe if the event organizer provides a certified, verifiable chain of custody directly from the manufacturer. Attendees should look for tamper-evident seals and use the manufacturer's official software to verify the device's authenticity upon first connection. If the device was sourced through a third-party reseller or the provenance is unclear, it should be treated as compromised and either discarded or used only for non-critical testing purposes.
How should event organizers vet tech hardware partners for international summits?
Organizers must conduct a comprehensive supply chain audit that goes beyond a simple vendor contract. This includes requiring direct-from-factory shipping, verifying the vendor's status as an 'Authorized Partner' on the manufacturer's official website, and including strict liability clauses in contracts. Additionally, organizers should request independent security audits or 'Know Your Vendor' (KYV) documentation to ensure the partner has robust internal security protocols to prevent employee-led tampering.
What role does professional event documentation play in brand recovery after a security crisis?
Professional documentation acts as a transparent audit trail of the event's safety measures. By capturing high-quality video of security protocols, hardware verification processes, and executive responses, a brand can provide visual proof of its due diligence. This content is essential for rebuilding trust with stakeholders and the public, as it demonstrates a proactive and professional approach to risk management rather than a reactive or opaque one.
What are the legal implications for event organizers if distributed hardware is compromised?
Organizers may face significant legal liability under 'duty of care' and consumer protection laws. If it is proven that the organizer failed to perform basic due diligence in sourcing hardware—such as buying from unverified third-party resellers to save costs—they could be held liable for the resulting financial losses of attendees. This makes the procurement process a legal and insurance priority, requiring specific riders for cyber and physical product liability.
Frequently Asked Questions
Is it safe to accept hardware wallets as event swag after the Ledger incident?
It is only safe if the event organizer provides a certified, verifiable chain of custody directly from the manufacturer. Attendees should look for tamper-evident seals and use the manufacturer's official software to verify the device's authenticity upon first connection. If the device was sourced through a third-party reseller or the provenance is unclear, it should be treated as compromised and either discarded or used only for non-critical testing purposes.
How should event organizers vet tech hardware partners for international summits?
Organizers must conduct a comprehensive supply chain audit that goes beyond a simple vendor contract. This includes requiring direct-from-factory shipping, verifying the vendor's status as an 'Authorized Partner' on the manufacturer's official website, and including strict liability clauses in contracts. Additionally, organizers should request independent security audits or 'Know Your Vendor' (KYV) documentation to ensure the partner has robust internal security protocols to prevent employee-led tampering.
What role does professional event documentation play in brand recovery after a security crisis?
Professional documentation acts as a transparent audit trail of the event's safety measures. By capturing high-quality video of security protocols, hardware verification processes, and executive responses, a brand can provide visual proof of its due diligence. This content is essential for rebuilding trust with stakeholders and the public, as it demonstrates a proactive and professional approach to risk management rather than a reactive or opaque one.
What are the legal implications for event organizers if distributed hardware is compromised?
Organizers may face significant legal liability under 'duty of care' and consumer protection laws. If it is proven that the organizer failed to perform basic due diligence in sourcing hardware—such as buying from unverified third-party resellers to save costs—they could be held liable for the resulting financial losses of attendees. This makes the procurement process a legal and insurance priority, requiring specific riders for cyber and physical product liability.